


Data governance key components explained
Previously, governance used to be a control on human behaviour, applied after the fact through reviews and audits. Now, it is the interface an autonomous system reads before it does anything.
Before an AI agent acts, it needs to know four things: what is classified as PII, what policies apply, who can access what, and what has been certified as trustworthy. Every one of those answers comes from a governance component.
Those components also must resolve at machine speed rather than at review-board speed. Most enterprises still build these data governance components in phases:
- Months 1 to 3, foundation: Framework, roles, and policies
- Months 4 to 9, core: Quality, catalog, and security
- Months 10 onwards: Integration and stewardship
- Ongoing, continuous: Training and measurement
This gets you to operational governance in 12 to 18 months, rather than a multi-year slog.
What are the fundamentals of the 10 data governance components?
Ten components turn raw data into something your teams can actually trust and use.
- Foundation components: These include framework, roles, policies. They set up how governance works.
- Core components: These include quality, catalog, security. They put controls in place.
- Advanced components: These include integration and stewardship. They help you scale.
- Continuous components: These include training and measurement. They keep things improving.
When these components work together, teams spend less time troubleshooting and more time on work that matters. The key is to start with a few high-value data domains, not to roll out governance across the entire company on day one.
| Component | What it does | Key elements | How you measure it | Priority |
|---|---|---|---|---|
| 1. Framework | Sets your goals and who gets to make decisions. | Strategic objectives, scope, guiding principles, and authority structure | Adoption rate across business units, alignment with business goals | Foundation |
| 2. Roles | Makes it clear who owns what. | Data Owner, Steward, Custodian, and Consumer role definitions | % of assets with assigned owners, issue resolution time | Foundation |
| 3. Policies | Spells out the rules for handling data. | Classification standards, retention schedules, privacy protections, and access controls | Compliance rate, violation count, and employee awareness | Core |
| 4. Quality | Keeps data accurate and reliable through automated checks. | Quality metrics, validation rules, profiling, cleansing workflows, dashboards | Quality score (target >95%), issue resolution time | Core |
| 5. Catalog | Gives everyone a single place to find, understand, and trust data. | Business glossary, metadata docs, lineage tracking, search | Catalog coverage, adoption rate, time-to-discovery | Core |
| 6. Security | Protects data from unauthorized access and breaches. | Access controls, encryption, breach detection, PII masking, privacy assessments | Incident frequency, compliance audit scores | Core |
| 7. Integration | Keeps data consistent across systems. | Standardized data models, API management, cross-system connectors | Cross-system consistency, integration, and uptime | Advanced |
| 8. Stewardship | Handles day-to-day quality and change management. | Schema change management, data dictionary upkeep, and impact assessment | Change success rate, stakeholder engagement | Advanced |
| 9. Training | Teaches people how to work with data properly. | Data literacy programs, role-based training, certifications | Completion rate (target >80%), literacy scores | Continuous |
| 10. Measurement | Tracks whether governance is actually delivering value. | Business impact tracking, compliance reports, maturity assessments, and ROI | Maturity score improvement, time-to-insight reduction | Continuous |
No component works alone. Each one builds on the others and feeds the next.
How do the 10 components connect with each other?
| Component | Depends on | Enables | Why the link matters |
|---|---|---|---|
| 1. Framework | Nothing (starting point) | All other components | Everything flows from strategy |
| 2. Roles | Framework | Policy enforcement, quality management | People need to know who does what |
| 3. Policies | Framework, Roles | Quality standards, security controls | Rules guide what the execution layer does |
| 4. Quality | Policies, Catalog | Reliable analytics, AI model training | Bad data in = bad decisions out |
| 5. Catalog | Framework, Roles | Discovery, self-service analytics | The central hub that everything connects to |
| 6. Security | Policies, Catalog | Risk reduction, compliance | Protects everything else you build |
| 7. Integration | Catalog, Quality | Cross-system consistency | Governance only works if it spans systems |
| 8. Stewardship | Roles, Training | Sustainable day-to-day operations | Culture change makes governance stick |
| 9. Training | Framework, Roles | User adoption | People power every component |
| 10. Measurement | All components | Continuous improvement | Proves governance is worth the effort |
Why do the data governance components matter for enterprise leaders in 2026?
Four things make governance urgent in 2026. AI needs governed data to work, breaches keep getting more expensive, teams waste too much time on bad data, and the companies that govern data well simply outperform those that do not. Let’s explore each aspect further.
AI initiative success
Gartner predicts organizations will abandon 60% of AI projects unsupported by AI-ready data through 2026, with 63% either lacking or unsure of the right data management practices.
Here’s why. Models process language. They don’t know that your company’s “active customer” excludes accounts in a 90-day grace period, or that revenue is recognized on a different basis in one region.
Governance supplies that meaning, and without it a model produces confident answers built on the wrong definitions.
Risk mitigation
IBM’s 2026 Cost of a Data Breach Report puts the global average breach at $4.99 million, up 12% year over year. One in four malicious breaches was AI-enabled, a 56% increase, and those incidents averaged $6 million.
92% of organizations that suffered an AI-related breach lacked proper AI access controls. Shadow AI, via unapproved AI tools, featured in 43% of incidents, up from 20%, at an average cost of $5.39 million.
On the flip side, organizations using AI and automation extensively in security saved $1.93 million per breach and cut 65 days off response time.
Operational excellence
McKinsey found that 30% of enterprise time is spent on non-value tasks caused by poor data. That is nearly a third of your workforce’s time wasted.
Stewardship changes shape here too. Agents absorb the documentation and tagging volume, and stewards move to approving, arbitrating, and setting the standards those agents follow.
Competitive advantage
The 2026 State of Data Integrity and AI Readiness study found organizations with formal governance programs are 21 percentage points more likely to report high trust in their data, at 71% versus 50%. They also report 19% better operational efficiency and 16% better revenue generation.
Governance pays for itself.
How can you build each component systematically?
Start with your framework, define who owns what, write the rules, automate quality checks, and measure what matters. The “crawl, walk, run” approach works because it shows value early and builds momentum.
| Phase | Timeline | Components | What you need first | Success Criteria |
|---|---|---|---|---|
| Phase 1: Foundation | Months 1–3 | Framework, Roles, Policies | Nothing | Executive buy-in secured, roles assigned, policies written |
| Phase 2: Core | Months 4–9 | Quality, Catalog, Security | Foundation done | Quality scores going up, catalog adoption >40%, security controls live |
| Phase 3: Advanced | Months 10–15 | Integration, Stewardship | Core running | Cross-system integration live, stewardship processes in place |
| Ongoing | Continuous | Training, Measurement | All of the above | Quarterly maturity reviews, training completion >80% |
Step 1: Set up your framework
Tie governance goals to business outcomes that matter, like AI readiness or passing regulatory audits. Pick the data domains that are most important to your business right now. Start there, not everywhere.
Example implementation: A financial institution’s framework might prioritize regulatory compliance (Basel III, GDPR), data quality for risk modeling, and transparency for audit requirements, with clear scope boundaries covering trading, retail banking, and compliance data.
Step 2: Define who owns what
Accountability without authority is a recipe for failure. Data Owners need the power to make decisions, not just the blame when things go wrong. Set up four role definitions, including:
- Data Owners are business leaders responsible for data domains. They’re accountable for data accuracy, completeness, and business value.
- Data Stewards are people managing day-to-day quality and policy compliance.
- Data Custodians are engineers who handle the technical aspects of controls, storage, and access management.
- Data Consumers refers to everyone using data, who must follow the rules. Every critical data asset should have an owner. If nobody owns it, nobody fixes it.
The role list is also expanding. A context steward is emerging alongside the data steward, focused on how data is understood and used rather than only on how it is managed and protected. In practice this is the person who decides that “active customer” means one thing across every agent that asks.
Step 3: Write policies people can actually follow
Vague policies fail. “Data must be classified” does not tell anyone what to do. “All datasets with PII must get a ‘Confidential’ tag within 48 hours of ingestion” does.
Embed policies into the tools your team already uses.
Step 4: Automate quality management
Manual quality checks don’t scale. Define what “good data” looks like for your organization: accuracy, completeness, timeliness, consistency. Then set up automated monitoring that catches problems before they reach anyone downstream.
Let quality checks run inside the warehouse itself, on Snowflake, Databricks, or BigQuery, so no new compute is provisioned and no data leaves the perimeter.
And use AI to draft the first version of a rule. This gets coverage past the top 200 tables into the long tail where most breakage actually happens. Atlan’s Data Quality Studio works this way.
Step 5: Measure business impact, not just compliance
Track things leadership cares about: time saved, costs avoided, revenue opportunities unlocked. “Number of assets tagged” will not hold anyone’s attention in a board meeting.
You must show the value of the investment or the risk of losing it to gain stakeholders’ support.
How do data governance components work together?
Data governance components work as a system, organized into four layers: foundation, execution, oversight, and enablement. The foundation layer components define scope, assign ownership, and write rules for the execution layer, which in turn feeds into trust signals and compliance evidence. The oversight layer components manage risk through regulatory alignment and deliver compliance proof. Lastly, enablement layer components drive adoption through continuous optimization.
Here’s an overview of how components in each layer feed into other components:
| Layer | Components | What it does | Key activities | What it feeds into |
|---|---|---|---|---|
| Foundation | 1–3 (Framework, Roles, Policies) | Sets direction | Define scope, assign ownership, and write standards | Rules for the execution layer |
| Execution | 4–7 (Quality, Catalog, Security, Integration) | Runs governance day to day | Automate controls, enforce policies, and help people find data | Trust signals and compliance evidence |
| Oversight | Spans components | Manages risk | Audit trails, regulatory alignment, risk reviews | Compliance proof |
| Enablement | 9–10 (Training, Measurement) | Drives adoption and improvement | Build data skills, track KPIs, and adjust the approach | Feedback for continuous optimization |
Foundation layer
Foundation layer components answer three questions: What data matters most? Who owns it? What rules apply? If those answers are unclear, everything downstream struggles.
Your strategy and scope determine which data needs governance and why. The operating model assigns accountability while policies and standards define the rules.
Execution layer
The Execution layer puts policies into practice through automation. Quality monitoring, catalog discovery, column-level lineage, and security controls all live here.
Think of data lineage as your company’s map. Data often takes five or six hops from a source system like Salesforce to a final BI dashboard. When something breaks, lineage lets you trace the problem in minutes instead of hours.
Technical components in the execution layer implement policies at scale:
- Quality management ensures data meets standards
- Metadata catalogs enable discovery and understanding
- Lineage tracks dependencies and impacts
- Security protects sensitive information
- Master data ensures cross-domain consistency
- Lifecycle management handles temporal aspects
Oversight and enablement layers
In the oversight layer, components provide audit support and regulatory alignment necessary to deliver compliance proof. They manage risk using audit trails and risk reviews.
Enablement layer components include tooling to automate execution and measurement, which drives continuous improvement.
Start with one or two high-value domains and prove that governance works. Then expand. The Precisely and Drexel University 2025 Outlook shows 71% of organizations now have some form of governance, up from 60% in 2023. But only 15% call theirs mature.
The difference between having a program and running a good one usually comes down to how well these layers connect.
Which enterprise data governance framework align with these components?
Three well-known frameworks map to these 10 components. They give you a head start, so you do not have to figure out everything from scratch.
| Framework | Covers components | Focus area | Maturity benchmark | Best for |
|---|---|---|---|---|
| DAMA-DMBOK | 1–3, 4–5, 6-7 | Data governance, metadata management, and security and integration disciplines. | 11 knowledge areas | Broad governance programs |
| ISO 8000 | 4, 10 | Quality and measurement | International certification | Quality-focused programs, global teams |
| NIST Privacy Framework | 6 | Security and privacy | Risk-based (Identify, Govern, Control, Communicate, Protect) | Regulated industries (healthcare, finance, government) |
DAMA-DMBOK framework integration
DAMA-DMBOK covers 11 knowledge areas and provides a solid blueprint for program design.
- Components 1-3 (Framework, Roles, Policies) align with DAMA’s Data Governance and Data Architecture disciplines
- Components 4-5 (Quality, Catalog) correspond to Data Quality Management and Metadata Management functions
- Components 6-7 (Security, Integration) map to Data Security and Data Integration disciplines
ISO 8000 standards compliance
ISO 8000 provides international benchmarks for data quality that apply across regions and teams.
- Provides international standards for data quality management that directly support Component 4
- Offers structured approaches for metadata management supporting Component 5
- Establishes quality measurement frameworks essential for Component 10
Enterprise context platforms like Atlan weave governance as a function of the context layer, and automate these standards into daily workflows.
NIST privacy framework application
For healthcare, finance, and government teams, NIST provides the compliance foundation.
- Governs Component 6 implementation with structured privacy risk management
- Provides assessment methodologies supporting Component 10’s measurement requirements
- Offers incident response frameworks complementing data security policies
Aligning your security component with NIST standards makes audit preparation faster and strengthens regulatory readiness.
Related reading: Data Governance Framework
How does governing AI extend these components?
Governing AI is not a second program. Data, context, and AI belong in one lifecycle rather than three, for the plain reason that GDPR connects to AI: the same personal data that triggers a subject access request is the data your model trained on and your agent retrieves.
The components don’t change. What changes is that each one now has to answer to a machine as well as a person.
| Component | What it covers today | What AI adds | Example |
|---|---|---|---|
| 1. Framework | Goals and scope | AI ethics principles, risk classification | EU AI Act compliance mapping, model risk tiers |
| 2. Roles | Owner, Steward, Custodian | Model Owner, ML Engineer accountability | Cross-functional AI governance councils |
| 4. Quality | Accuracy and completeness checks | Bias detection, model drift, and fairness metrics | Demographic parity testing, ongoing model validation |
| 5. Catalog | Data asset discovery and lineage | AI model registry, feature stores, training data lineage | Model-to-data lineage, experiment tracking |
| 6. Security | Access controls, encryption | Algorithmic audit trails, explainability | SHAP values, model decision logging |
| 8. Stewardship | Data quality ownership | Model performance monitoring | MLOps and data stewardship working together |
| 9. Training | Data literacy programs | AI governance literacy, model risk awareness | Responsible AI training for business users |
| 10. Measurement | Data quality KPIs | Model performance, fairness KPIs | Bias audits, model ROI tracking |
Deloitte’s 2026 State of AI in the Enterprise found 23% of companies use agentic AI at least moderately today and 74% expect to within two years. Only 21% report a mature governance model for autonomous agents. Data privacy and security is the top-cited AI risk at 73%.
Governing the AI is not really about governing the AI. To govern the AI you need to govern the context it reads.
Should you choose open-source or enterprise platforms?
When choosing tools for data quality, catalog, security, and integration, teams must decide between open-source and enterprise platforms. Open-source tools cost less up front and offer more flexibility, but they require significant engineering effort to maintain and integrate. Enterprise platforms cost more upfront, but they offer built-in compliance reporting, a unified user experience, and vendor support. At scale, they often reduce the total cost of ownership.
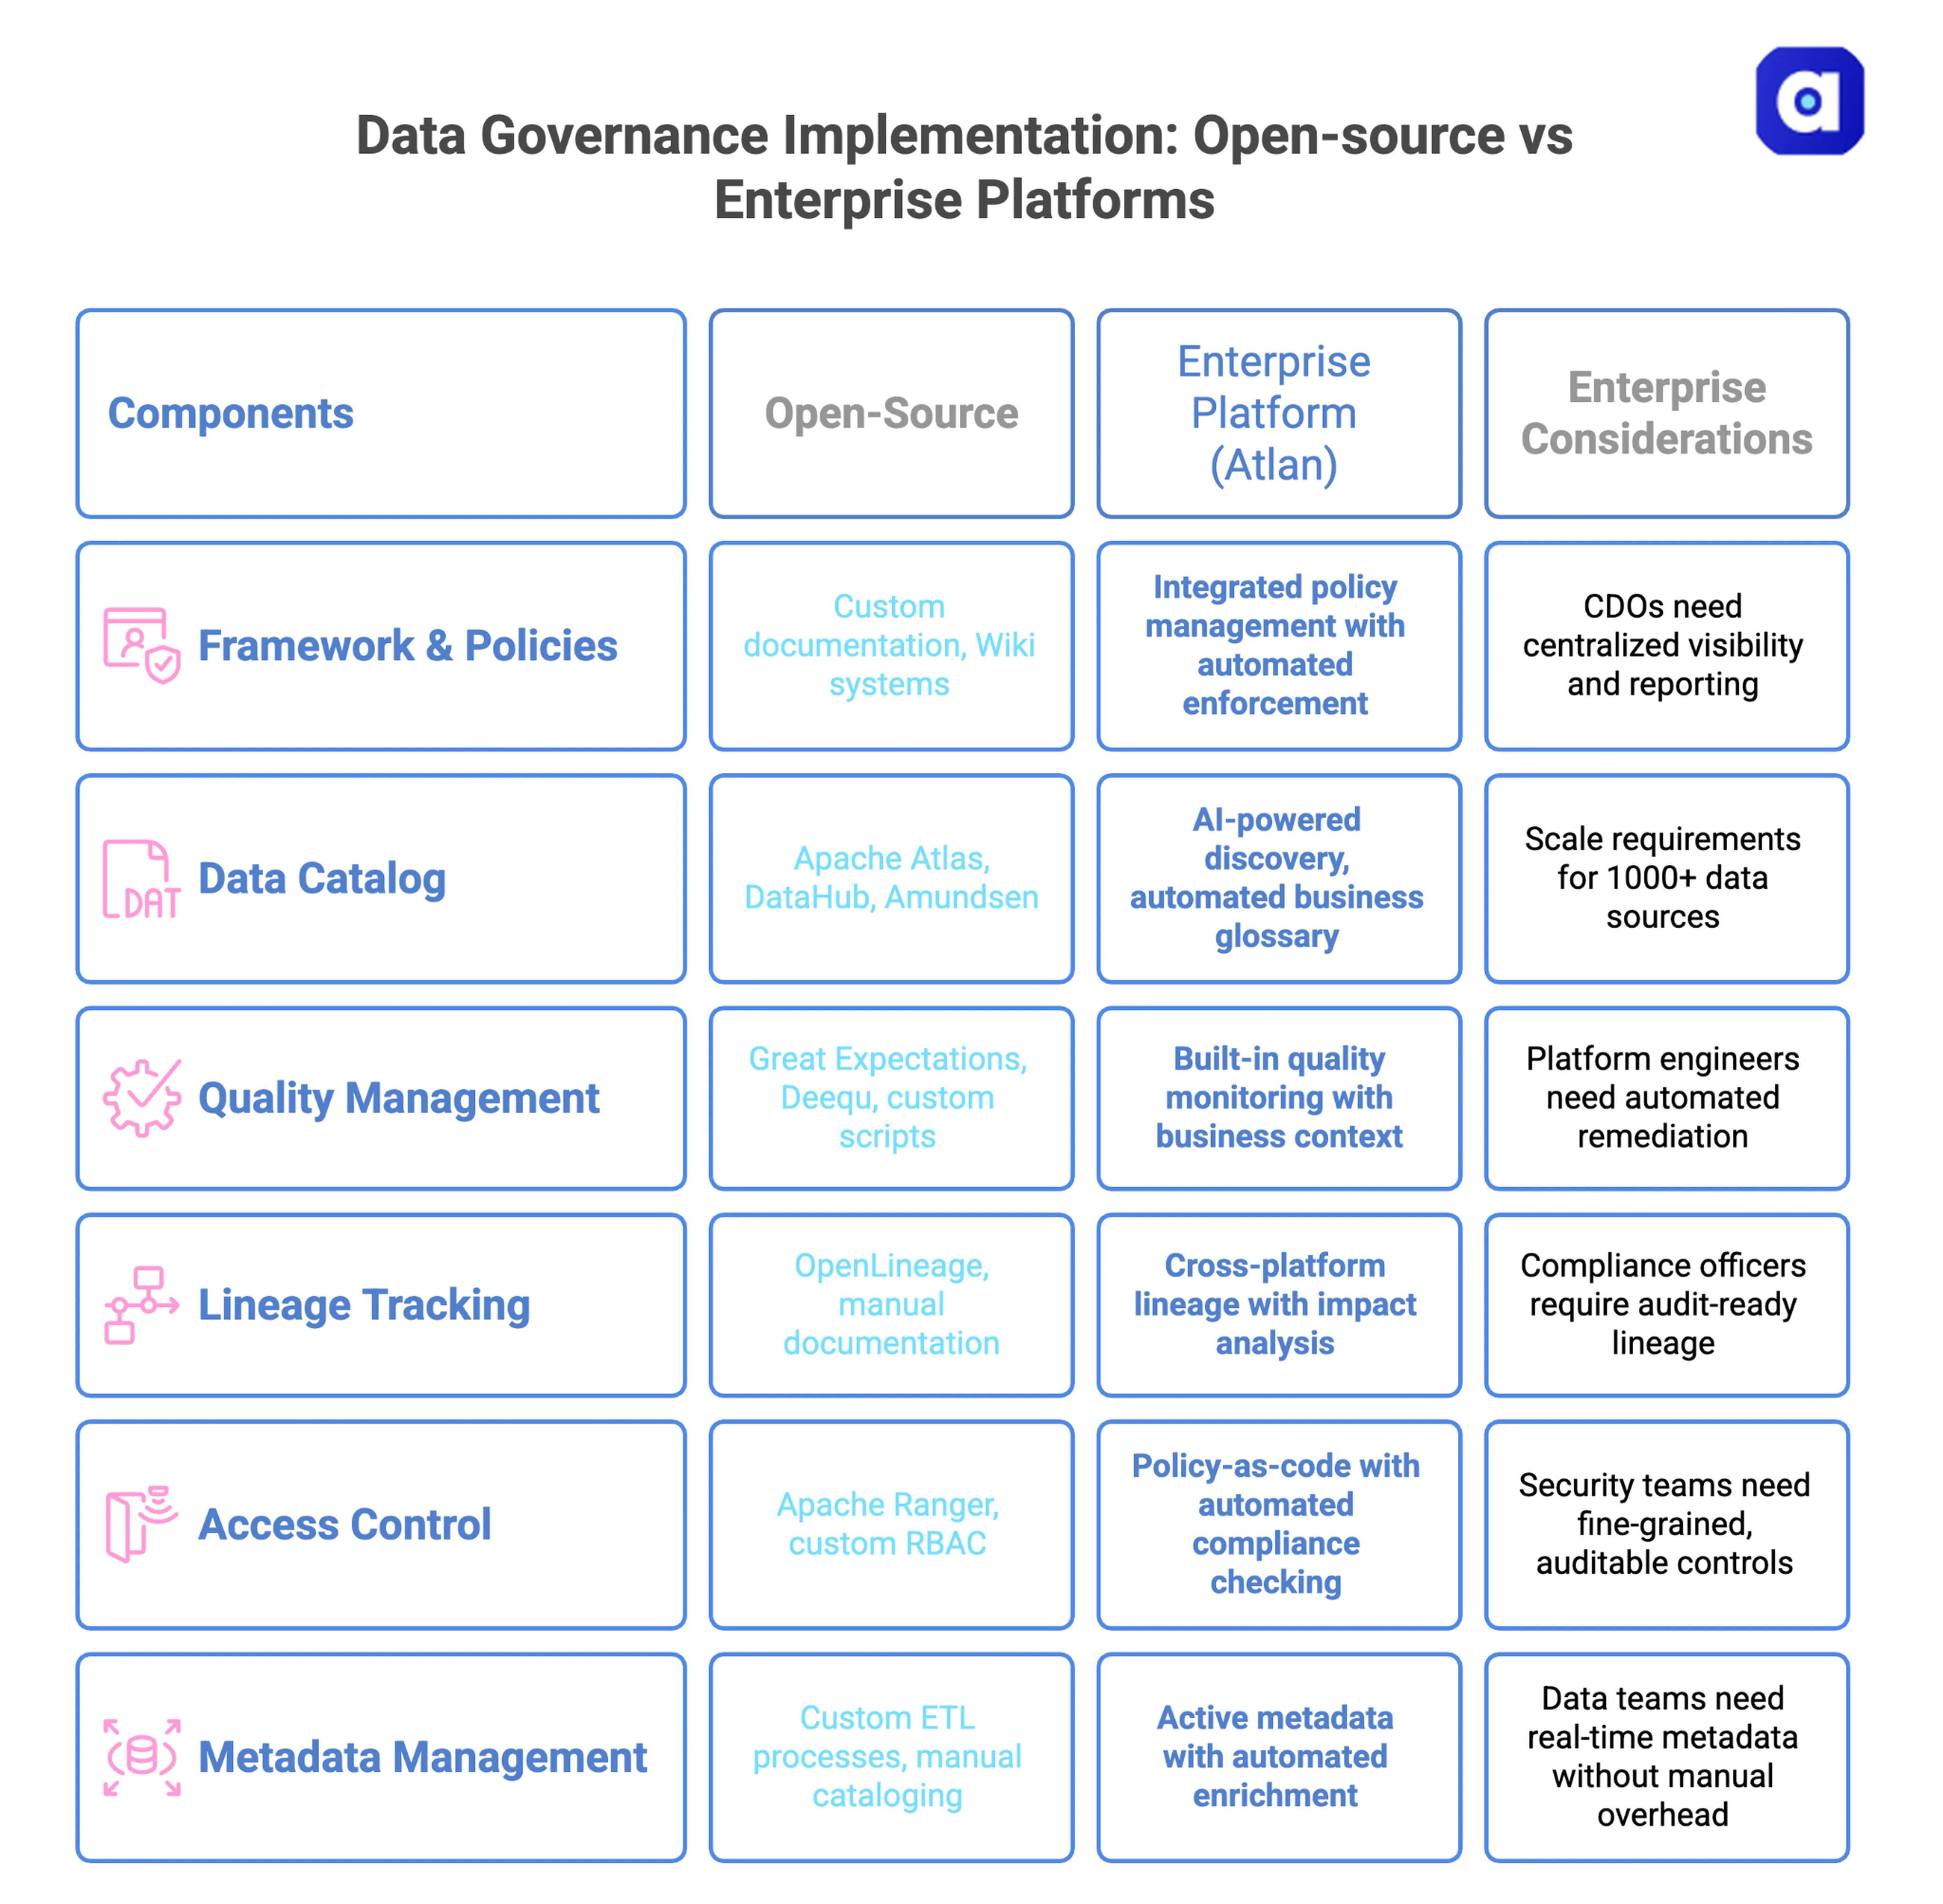
Open-source works well for teams with strong engineering and simpler governance needs. Enterprise platforms make more sense when you need automated compliance, broad integration, and high adoption. For large-scale rollouts, total cost of ownership often favors managed platforms because they cut engineering overhead and automate compliance reporting.
Adoption comes down to one thing: meeting people where they work. If 40% of users drop off at the login screen of a separate tool, the program has failed. The platform needs to appear within the tools your team already uses.
Related reading: What is a Data Catalog?
How does Atlan approach the key components of data governance?
Most governance programs stall because each component lives in a different tool. The catalog sits in one place, quality monitoring in another, policy in a third. Stewards move between interfaces, enforcement drifts, and measuring anything means pulling exports from four systems.
Atlan is the context layer for AI, the infrastructure that makes enterprise AI accurate, trustworthy, and scalable. Governance is a function inside that layer rather than the category Atlan occupies. The ten components resolve into one governed context surface that people and agents both read from, under the same entitlements.
-
Context Agents, components 1, 2, 3, and 9: Context Agents autonomously author descriptions, READMEs, glossary terms, metrics, and semantic models, then route them to stewards for approval.
Work that took 9 to 12 months of manual stewardship now rolls out in around 30 days. One accelerator cohort avoided more than 55,000 hours of manual work in a single week, and 64% of the customer base adopted within three months at 7x higher value realization.
-
Data Quality Studio, component 4: Data Quality Studio is the first native quality experience on Snowflake, Databricks, and BigQuery. Checks run in-warehouse, AI drafts first-version rules, no new compute is provisioned, and no data leaves the perimeter.
-
Context Lakehouse, components 5 and 7: The Context Lakehouse persists assets, policies, lineage, and quality signals as Apache Iceberg tables behind a Polaris REST catalog. Queryable from Snowflake, Databricks, Spark, or Athena, with no proprietary export, so your context stays in an open format you own.
-
Policy Center, components 3 and 6: Classification, masking, and entitlements resolve once and apply everywhere, including at agent inference time. Policy as code is what lets an agent operate without a human approving each request.
-
Atlan MCP and conversational AI, components 5 and 6: The MCP server and conversational AI serve context to humans and agents at inference under identical persona entitlements. Atlan recorded more than 8 billion context reads in 90 days and 58x growth in monthly MCP calls since September 2025.
-
Context Engineering Studio, components 8 and 10: Context Engineering Studio versions, simulates, and grades agents before deployment, deriving test cases from downstream lineage. Workday and Fox each report 5x better AI analyst accuracy on governed Atlan context.
-
App Framework and Marketplace, component 7: Partners including Immuta, BigID, and Cyera ship apps as first-class citizens on the App Framework, with more than 40 marketplace apps available by February 2026. Atlan stays neutral across Databricks, Snowflake, and Microsoft rather than pulling you into one stack.
One measured result ties this together. Atlan Frontier Labs found governed context lifted natural-language query accuracy by 38% across 174 enterprise queries and 522 evaluations. The gain came from governance, not from a bigger model.
Real stories from real customers building context layers with Atlan

Modernized data stack and launched new products faster while safeguarding sensitive data
"Austin Capital Bank has embraced Atlan as their Active Metadata Management solution to modernize their data stack and enhance data governance. Ian Bass, Head of Data & Analytics, highlighted, 'We needed a tool for data governance… an interface built on top of Snowflake to easily see who has access to what.' With Atlan, they launched new products with unprecedented speed while ensuring sensitive data is protected through advanced masking policies."

Ian Bass, Head of Data & Analytics
Austin Capital Bank
🎧 Listen to podcast: Austin Capital Bank From Data Chaos to Data Confidence
Curious which components could unlock the same speed for your team?
Book a Personalized Demo
53 % less engineering workload and 20 % higher data-user satisfaction
"Kiwi.com has transformed its data governance by consolidating thousands of data assets into 58 discoverable data products using Atlan. 'Atlan reduced our central engineering workload by 53 % and improved data user satisfaction by 20 %,' Kiwi.com shared. Atlan's intuitive interface streamlines access to essential information like ownership, contracts, and data quality issues, driving efficient governance across teams."
Data Team
Kiwi.com
🎧 Listen to podcast: How Kiwi.com Unified Its Stack with Atlan

One trusted home for every KPI and dashboard
"Contentsquare relies on Atlan to power its data governance and support Business Intelligence efforts. Otavio Leite Bastos, Global Data Governance Lead, explained, 'Atlan is the home for every KPI and dashboard, making data simple and trustworthy.' With Atlan's integration with Monte Carlo, Contentsquare has improved data quality communication across stakeholders, ensuring effective governance across their entire data estate."

Otavio Leite Bastos, Global Data Governance Lead
Contentsquare
🎧 Listen to podcast: Contentsquare's Data Renaissance with Atlan
Moving forward with data governance key components
If you are starting from scratch, start with the foundation tier. Get executive backing, assign owners for your two or three most important domains, and write the policies that your regulatory context actually requires. Proving value in one domain builds the credibility to expand into the next.
Two shifts are worth planning for now. The first is that agents, not people, become the highest-volume consumer of your governance decisions, which means every component has to answer in milliseconds and in a machine-readable form.
The second is cultural rather than technical: stewardship moves from documenting data to approving what agents have documented, and domains take on their own artefacts instead of waiting on a central team.
Book a demo to see how Atlan’s enterprise context layer helps you set all this up under one roof.
FAQs about data governance components
1. Which components should you prioritize in your governance roadmap?
Start with the Foundation: framework, roles, and policies. These three cost the least, take the least time, and unlock everything else. Once they are solid, add Core components one domain at a time. Show value before you expand. AI governance is not a separate project in 2026. It is part of what you are already building. Every framework, quality check, and catalog entry you set up today becomes the foundation your AI efforts need tomorrow. Your roadmap does not need to be complicated. It needs to be intentional.
2. What’s the biggest mistake organizations make with governance roles?
Assigning accountability without authority. Data Owners need decision-making power, not just responsibility for outcomes they can’t control.
Give them real decision-making power over their domains. It includes the authority to block data assets that do not meet quality thresholds.
3. Why do governance policies often fail to stick?
A governance policy in a document nobody opens is just words. Build policies into the tools your team uses every day: GitHub for developers, Slack for communication, BI tools for analysts. If following governance means leaving your workflow, most people will not bother.
4. How do technical implementations go wrong?
Buying a complex platform before you know what you need wastes money and time. Start with one high-value use case that shows quick ROI. A single well-governed data domain opens the door. An 18-month platform build that launches to low adoption does not.
5. What causes governance programs to lose momentum?
If you only track technical metrics like “number of assets tagged,” executives will tune out. Measure and communicate business impact: time saved, costs avoided, revenue unlocked. Trust comes from transparency. When a pipeline breaks, tell people right away. “The pipeline failed today, do not use the dashboard,” builds more trust than silence.
6. Does AI change which data governance components I need?
The same 10 components still apply. AI just adds new needs to each one. Component 4 (quality) grows to include bias detection and model drift monitoring. Component 5 (catalog) adds AI model registries and feature stores. Component 6 (security) picks up algorithmic audit trails and explainability. The ones doing it well layer AI controls onto existing components instead of starting from scratch.
7. Why do automation promises disappoint?
Because tools that only execute policy get sold as tools that set it. Execution without policy setting and enforcement leaves the hard decisions unmade, and the program looks automated while the backlog grows.
Current automation is also not mature enough to run without people. The credible model is human on the loop: agents do the volume work of documenting, tagging, classifying, and drafting rules, and stewards approve, arbitrate, and set standards. The preposition matters. Human in the loop means a person at every step, which does not scale. Human on the loop means a person over the process, which does.
8. What metrics prove governance is working?
Track business outcomes rather than technical activity. Useful measures include reduction in data incidents, analyst time saved, audit preparation time, AI answer accuracy, and data-user satisfaction. Asset-tagging counts will not hold a board’s attention. If governance does not reduce risk, save time, or release revenue, it is not delivering value.
9. Should governance start centrally or within business domains?
Start centrally for standards and decision rights. Execute within domains for speed and ownership. A federated model works best. The central team defines policies and quality thresholds. Domain teams apply them to their own datasets. This balances consistency with agility.
Sources
Gartner | Newsroom | Lack of AI-Ready Data Puts AI Projects at Risk https://www.gartner.com/en/newsroom/press-releases/2025-02-26-lack-of-ai-ready-data-puts-ai-projects-at-risk
IBM | Newsroom | One in Four Malicious Breaches are AI-Enabled, Costing Companies $6 Million on Average https://newsroom.ibm.com/2026-07-29-ibm-study-one-in-four-malicious-breaches-are-ai-enabled,-costing-companies-6-million-on-average
IBM | Reports | Cost of a Data Breach Report https://www.ibm.com/reports/data-breach
Drexel LeBow | Center for Applied AI and Business Analytics | 2026 State of Data Integrity and AI Readiness https://www.lebow.drexel.edu/sites/default/files/2026-01/lebow-precisely-state-data-integrity-ai-readiness-2026.pdf
McKinsey | Digital | Designing Data Governance That Delivers Value https://www.mckinsey.com/capabilities/mckinsey-digital/our-insights/designing-data-governance-that-delivers-value
Precisely | Resource Center | 2026 State of Data Integrity and AI Readiness https://www.precisely.com/resource-center/infographics/state-of-data-integrity-and-ai-readiness-2026/
Deloitte | AI Institute | State of AI in the Enterprise: The Untapped Edge https://www.deloitte.com/content/dam/assets-zone3/us/en/docs/services/consulting/2026/state-of-ai-2026.pdf
