

What are the essential factors of a data governance policy?
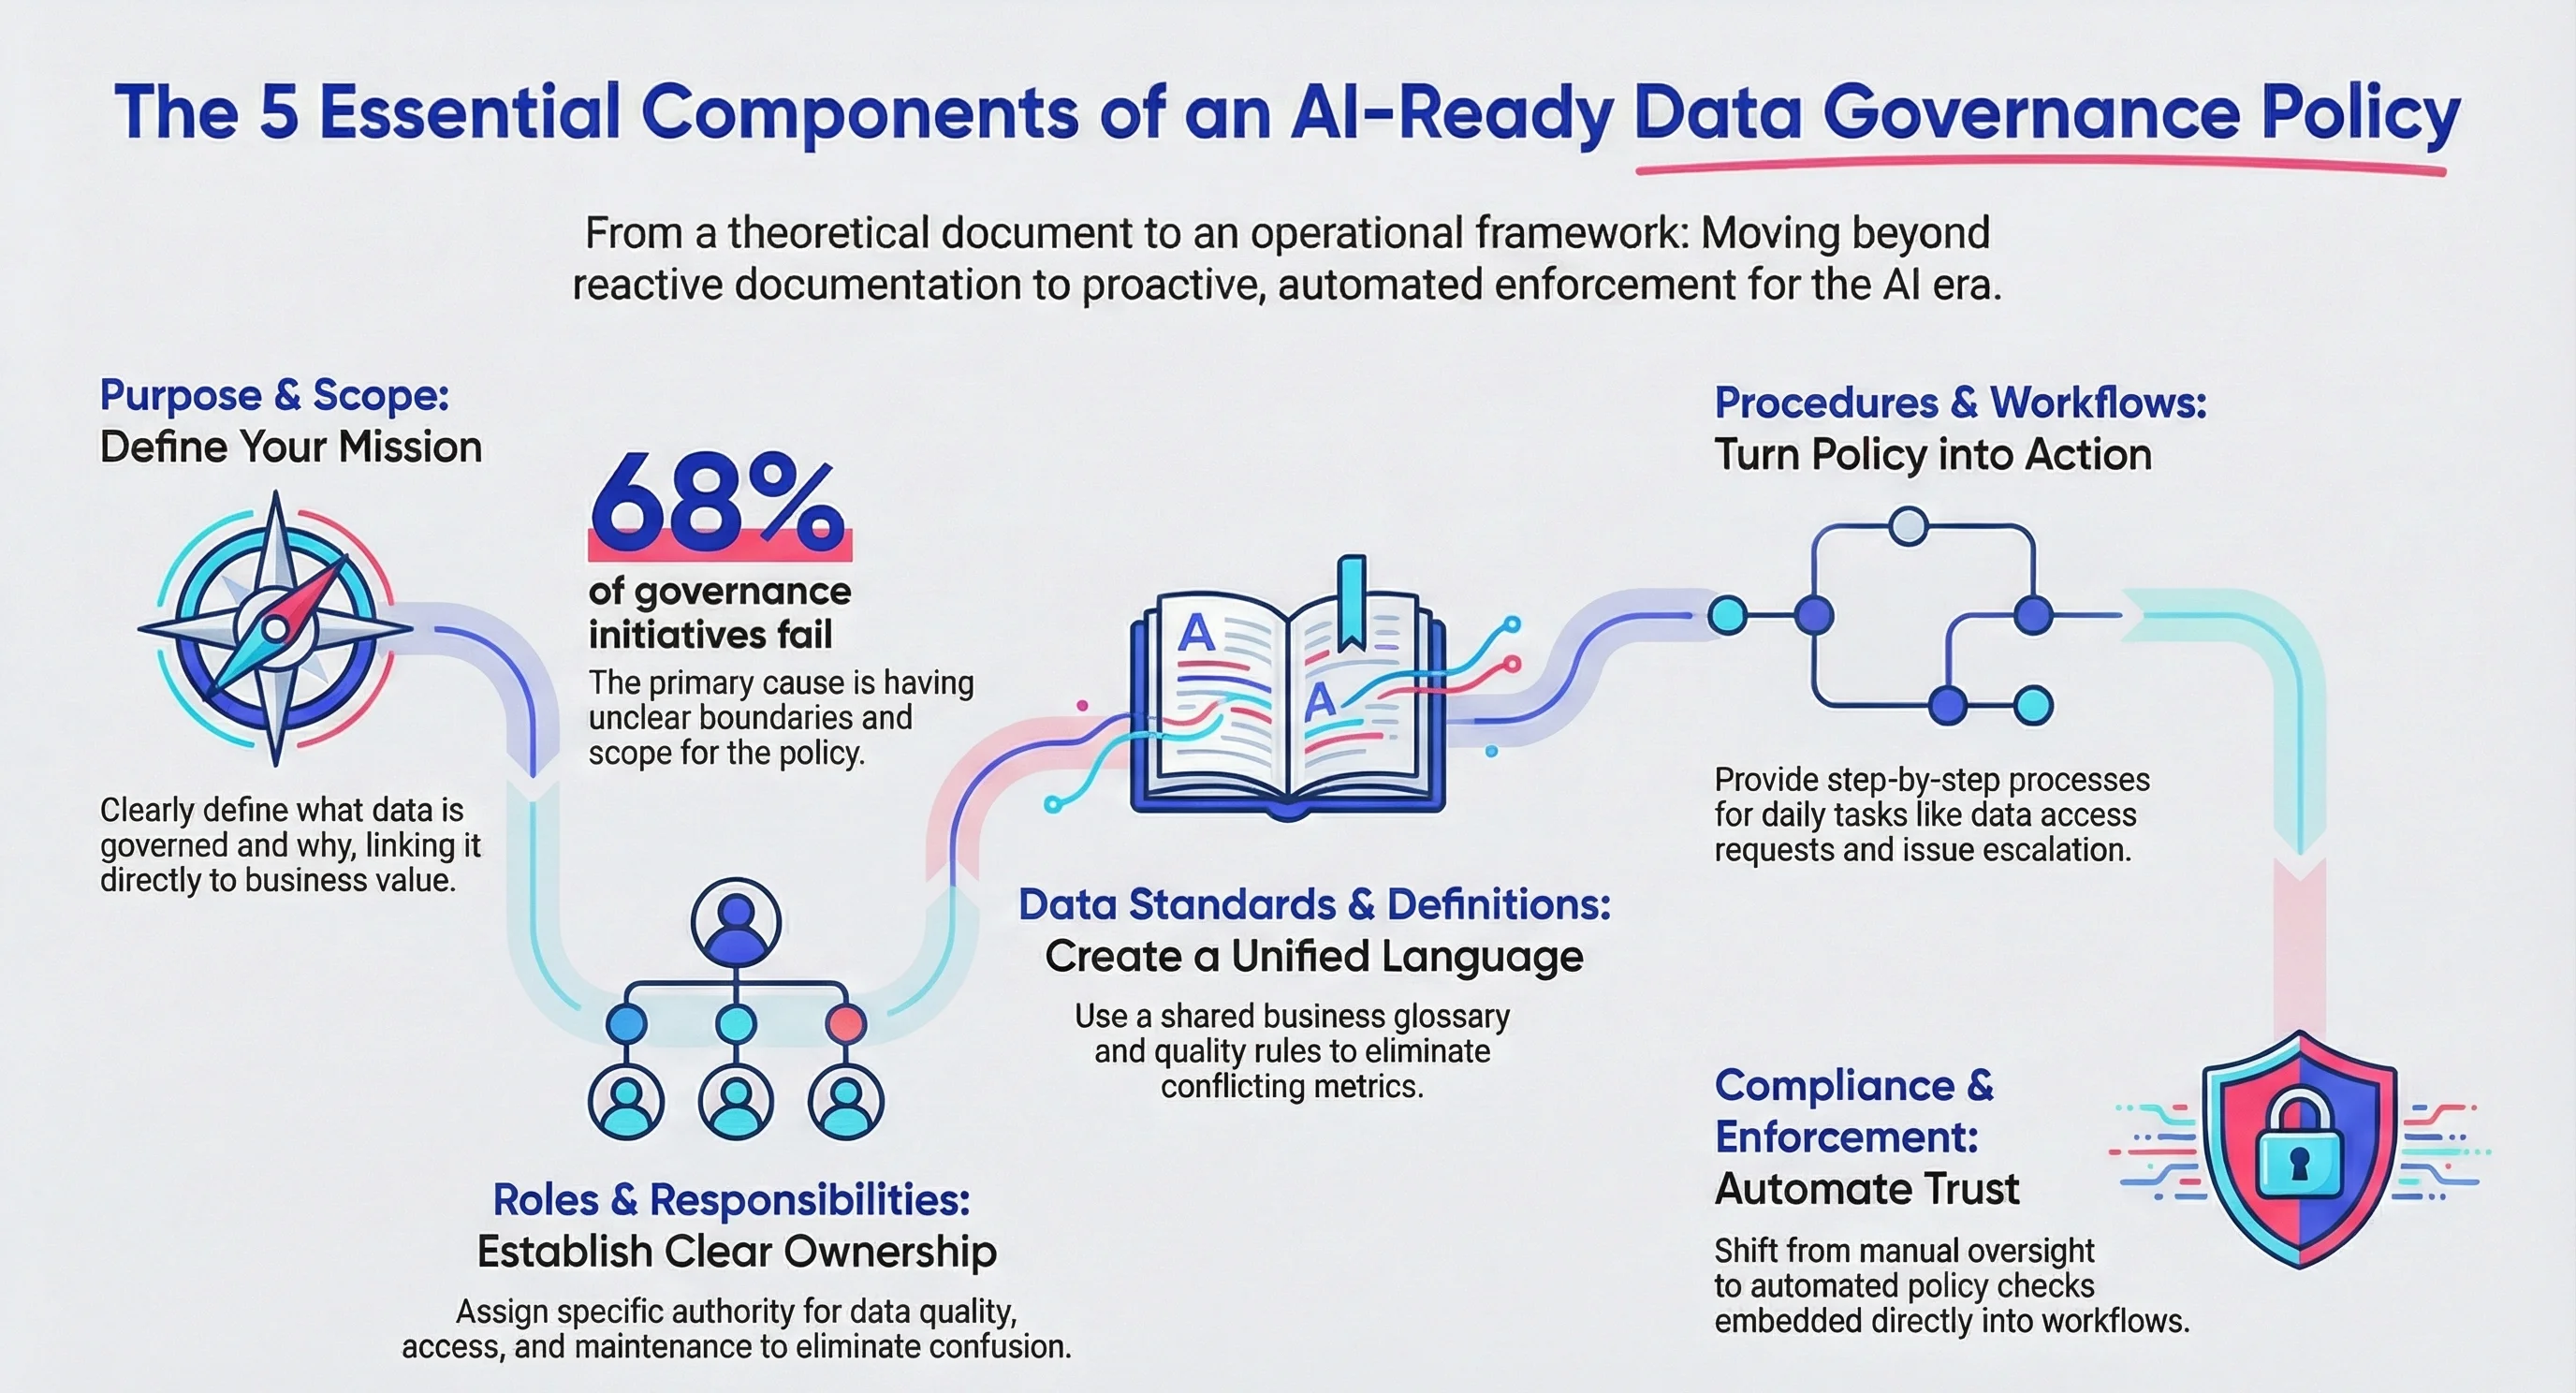
An agent inherits the governance rules of the data it reads. Without governance, agents leak data they shouldn’t. A data governance policy is where those rules get written down so they apply consistently. A comprehensive data governance policy consists of five core sections that transform governance from theory into operational practice.
1. Purpose and scope
Define exactly what you’re governing and why it matters to your bottom line. This section answers the questions that prevent scope creep and secure stakeholder buy-in.
What to include:
- Specific business objectives: improve data quality for ML models, meet GDPR compliance, or reduce security risk
- Precise data boundaries: “Customer PII in production databases,” not “customer information”
- Clear exclusions that prevent mission creep
- A direct line to revenue impact or risk mitigation
A governed context layer can define scope programmatically, automatically classifying data assets by sensitivity and applying the right policy without manual documentation.
Why data teams struggle here: Vague scope statements create endless debate about coverage. Gartner predicts that 80% of data and analytics governance initiatives will fail by 2027, largely because they aren’t tied to a real business outcome. Be specific about what’s covered, and why, to keep teams from making costly assumptions.
2. Roles and responsibilities
Clear ownership prevents the “not my job” problem that kills governance initiatives. This section removes ambiguity about decision-making authority and daily execution.
Essential role definitions:
- Chief data and AI officer: business alignment, resource allocation, and executive sponsorship
- Data Governance Council: strategic oversight and policy approval
- Data owners, accountable for a specific business domain
- Data stewards making day-to-day quality and access decisions within that domain
- Data custodians handling technical implementation and maintenance
- Data users, who carry consumption responsibilities and escalation duties
Critical success factor: Map each data lifecycle stage to a specific role. Who approves new data sources? Who resolves quality issues? Who grants access? Federated models work best: domain teams own quality while central teams maintain consistency standards.
3. Data standards and definitions
This section eliminates conflicting metrics across teams. Without shared definitions, an organization ends up with parallel versions of the truth that undermine decision-making.
Core components:
- A semantic layer holding official definitions for key terms and metrics, mapped to how the business actually talks
- Quality thresholds for accuracy, completeness, and timeliness, enforced inside the context layer
- Naming conventions for datasets and fields, propagated automatically across the enterprise data graph
- Classification schemas: sensitivity levels (public, internal, confidential, restricted) tagged once and inherited everywhere
- Master data hierarchies: authoritative sources for customers, products, and locations, connected through the graph
Real-world impact: When marketing’s “active customer” definition differs from finance’s, executive dashboards show conflicting numbers. Standardized definitions prevent these trust-destroying scenarios. A governed context layer propagates a definition to every downstream asset automatically, so consistency doesn’t depend on someone remembering to update a second document.
essential components of a data governance policy - Image by Atlan.
4. Procedures and workflows
Turn policy statements into step-by-step processes teams can execute without needing to ask for clarification. This section bridges governance theory and daily operations.
Essential workflows:
- Data access requests, with clear approval paths and defined timeframes
- Quality issue escalation: who to contact when data breaks
- New dataset onboarding: security, quality, and documentation requirements
- Change management for modifying existing data structures safely
- Exception handling for when and how to deviate from standard procedure
Implementation keys: Include specific timeframes, such as a 48-hour approval SLA, required documentation, and automated workflow triggers where possible.
5. Compliance and enforcement
Without enforcement, a policy is just documentation. This section defines how governance translates into measurable outcomes and behavioral change.
Enforcement mechanisms:
- Policy as code: governance rules written as executable logic that runs inside data pipelines, blocking non-compliant operations before they reach production
- Automated classification: ML and rule-based tagging of sensitive data at ingestion, so policy attaches to the right assets from day one
- Access control through RBAC and ABAC models that restrict data by role, sensitivity, and context like location or purpose
- Automated monitoring for real-time policy violation detection
- Audit schedules backed by immutable logs of every enforcement action, policy change, and access decision, for regulatory reporting
- Role-specific governance training requirements
- Violation consequences that escalate progressively, from a warning to access removal
- Success metrics that make governance effectiveness measurable
Modern approach: Shift from punitive to enabling enforcement. Build policy checks into existing workflows instead of standing up separate compliance processes, so following the rule is the easier path, not the harder one.
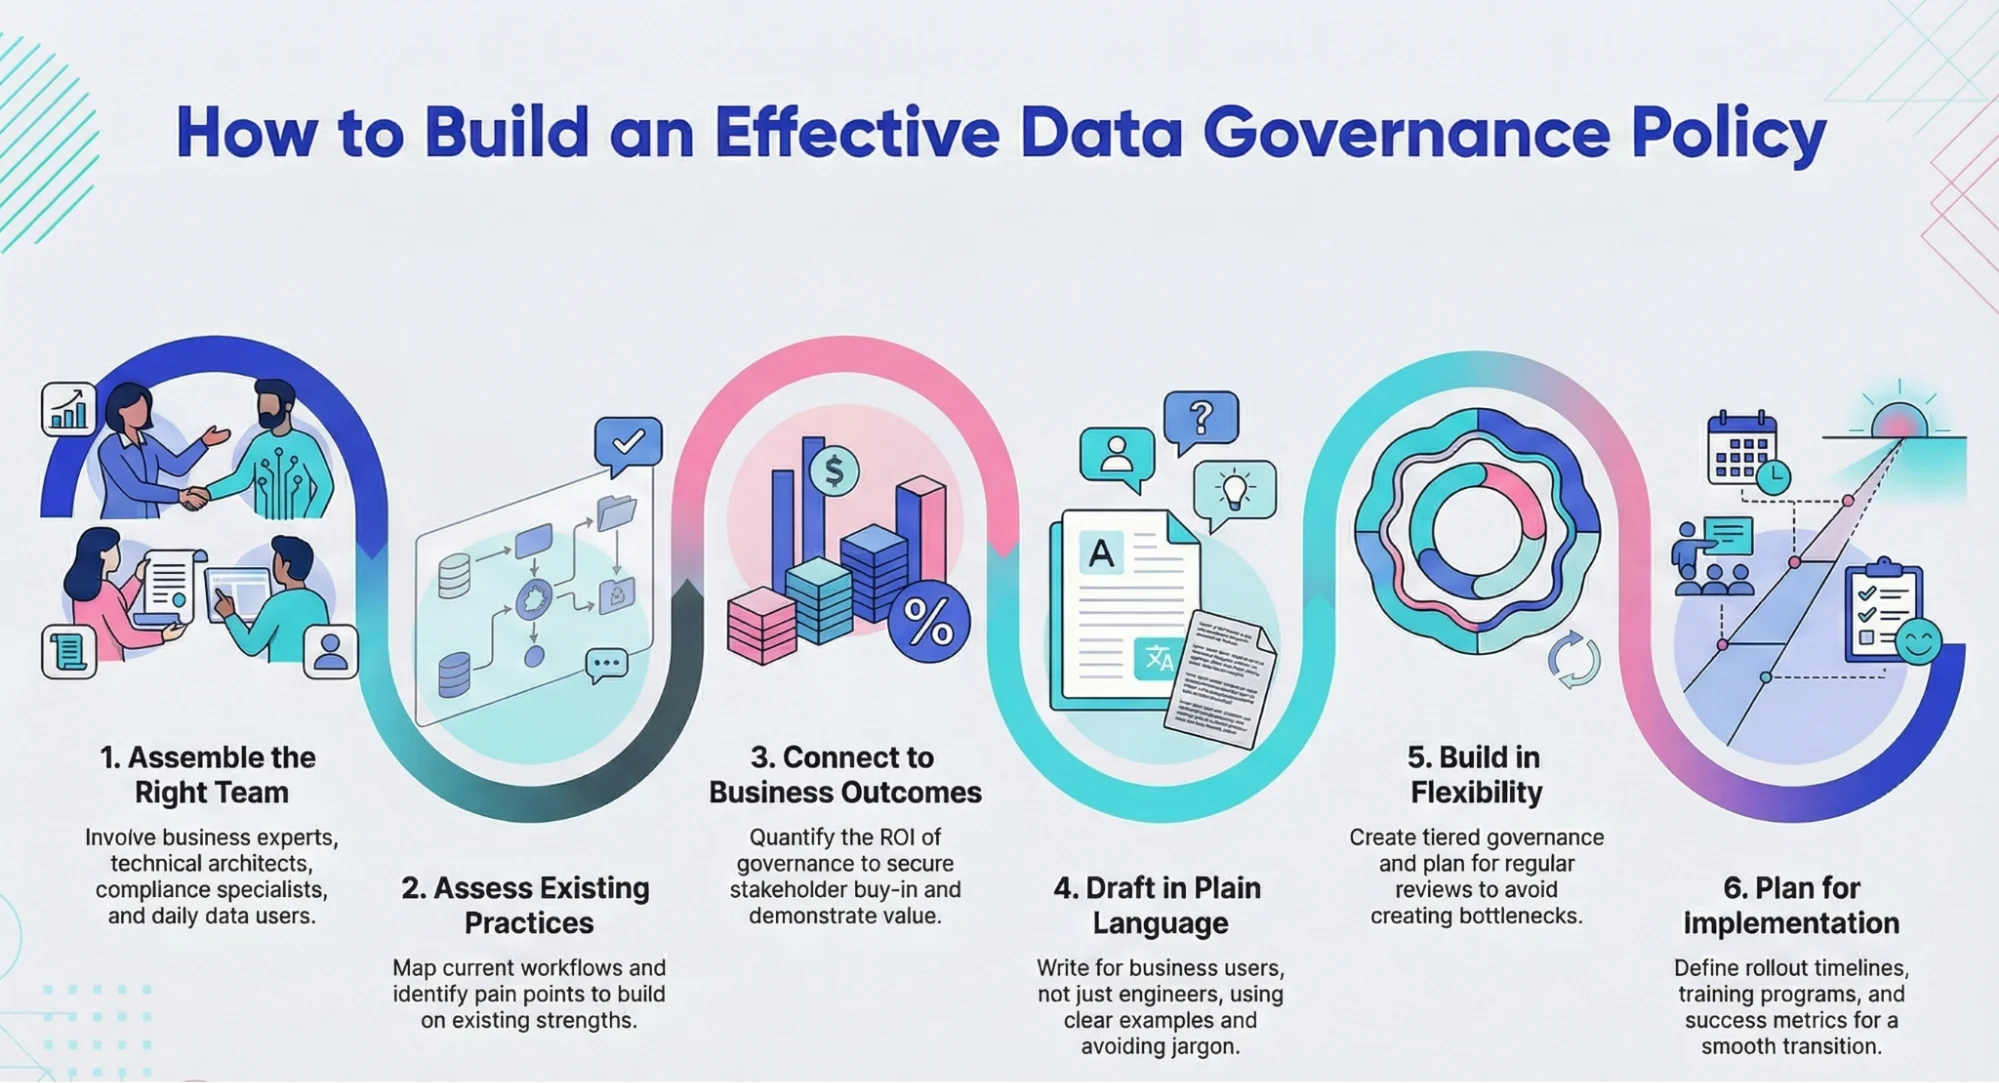
How to write a data governance policy: A 6-step guide
Modern data teams need policies that enable work, not create bottlenecks. Here’s the approach:
1. Assemble the right team
Include business domain experts, technical architects, compliance specialists, an executive sponsor, and actual end users. The biggest failures happen when governance teams write rules without input from the people who use data daily.
2. Assess existing practices
Document what’s already working before writing new rules. Map current workflows, identify pain points through conversations with the team, and review recent incidents so the policy builds on what already works instead of starting from a blank page.
3. Connect to business outcomes
Calculate the cost of poor data quality and show how governance accelerates AI initiatives. Stakeholders who see the business case champion the policy instead of resisting it.
4. Draft in plain language
Write for business users, not data engineers. Use concrete examples, organize it logically, and hold the whole document to 10 to 15 pages. A policy nobody reads doesn’t govern anything.
5. Build in flexibility
Set tiered governance based on data sensitivity, with a clear exception process and quarterly reviews. Policy as code makes this practical, since a stricter rule on one domain doesn’t require rewriting the whole policy.
6. Plan for implementation
Include a phased rollout timeline, role-specific training, required tools, and success metrics. The best policies create a direct path from documentation to daily practice.
How to build an effective data governance policy - Image by Atlan.
How to implement a data governance policy
1. Define clear approval authority
Data governance policies typically follow a hierarchical approval path:
- Data Governance Committee: reviews and recommends
- Executive sponsor, often the chief data and AI officer: validates business alignment
- Board of Directors or executive leadership: gives final approval for enterprise-wide policies
For domain-specific policies, approval might stop at the department head level, while enterprise policies affecting multiple departments need C-suite sign-off.
2. Establish enforcement responsibility
The enforcement model typically includes:
- Data stewards, who monitor adherence in their domain
- A data governance office that coordinates enforcement activity
- Automated systems that flag policy violations in real time
- Audit teams that verify compliance periodically
- IT security, which enforces access-related policies
The most successful enforcement models run what Gartner calls “just-in-time governance”: policy checks embedded directly into the workflow where data is created or accessed, not bolted on as a separate process afterward.
3. Roll out in phases
Start with high-impact, low-complexity policies on your most critical data assets, prove the value, then expand scope from there. Trying to implement everything enterprise-wide at once overwhelms teams and guarantees resistance.
Regulatory compliance in your data governance policy
Effective policies must harmonize with regulatory frameworks:
- GDPR alignment requires addressing data subject rights, lawful processing basis, impact assessments, breach notifications, and data minimization principles. Organizations handling EU citizen data need explicit consent mechanisms and data portability features built into policy workflows.
- CCPA/CPRA alignment needs consumer access and deletion rights, opt-out mechanisms, service provider requirements, and data inventory maintenance. California regulations require organizations to respond to consumer requests within 45 days, necessitating automated request handling.
- SOC 2 alignment covers access controls, change management, risk assessments, monitoring requirements, and incident response protocols. Service organizations must demonstrate continuous compliance through audit trails and policy enforcement logs.
Create policy frameworks that accommodate the strictest requirements while enabling region-specific variations. Map policies to specific regulatory requirements for clear compliance traceability.
Data governance policy templates and examples
If your organization is in the early stages of establishing best practices and standards around data, knowing where to start with your data governance policy can be challenging. Here are publicly-available data governance policies you can use as models:
- Oklahoma Office of Management & Enterprise Services offers comprehensive policy coverage with specific focus on governance roles and responsibilities.
- New Hampshire Department of Education provides detailed job duties for key individuals and outlines intended policy outcomes for measuring success.
- University of New South Wales Sydney demonstrates the multi-policy approach, separating standard data governance from research data governance for distinct requirements.
- East Carolina University demonstrates concise yet comprehensive coverage: scope, roles, and accountability in a short, precise document.
- Brandeis University ties every data source to a specific “data trustee,” ensuring complete ownership coverage across the data estate.
- University of Nevada Las Vegas includes comprehensive sections on data access, usage, and integrity standards.
Choose the template that best matches your organizational communication style and goals, or combine strengths from multiple examples.
How does an enterprise context layer automate data governance policy enforcement?
Manual governance can’t keep pace with the speed and scale of modern data. Reviews, spreadsheets, and periodic audits create delays, inconsistencies, and blind spots, and issues often surface only after the damage is already done.
A governed context layer like Atlan automates enforcement by tying governance rules directly to data assets. Policy activates instantly based on sensitivity, lineage, and usage, so access controls and masking apply the moment sensitive data appears, whether a person or an AI agent is the one requesting it.
The context layer monitors access continuously, flagging violations in real time instead of weeks later, and automated lineage mapping makes the downstream impact of a policy change clear immediately.
Real stories from real customers: Governance policy enforced through context
"AI initiatives require more context than ever. Atlan's metadata lakehouse is configurable, intuitive, and able to scale to hundreds of millions of assets. As we're doing this, we're making life easier for data scientists and speeding up innovation."
— Andrew Reiskind, Chief Data Officer, Mastercard

"Context is the differentiator. Atlan gave our teams the shared vocabulary and lineage to move from reactive data management to proactive AI enablement."
— Kiran Panja, Managing Director, Cloud and Data Engineering, CME Group

Moving forward with data governance policy
Effective data governance balances control with enablement. Define clear objectives tied to business outcomes, then map decision rights to each stage of the data lifecycle. The strongest policies rely on automation, embedding compliance checks into everyday workflows instead of adding extra oversight on top of them.
A governed context layer enforces rules at the point of data creation and use, for people and AI agents alike, shifting governance from reactive documentation to proactive risk management.
FAQs about data governance policy
1. What are the key components of a data governance policy?
A data governance policy typically includes purpose and scope, roles and responsibilities, data standards and definitions, procedures and workflows, and compliance enforcement mechanisms. Together, these give an organization clarity and accountability in how it manages data.
2. How can I implement a data governance policy in my organization?
Start by assessing existing practices, identifying key stakeholders, and drafting the policy collaboratively rather than in isolation. Align it with business objectives, then build a framework for monitoring compliance. A phased rollout with visible executive sponsorship consistently outperforms an all-at-once launch.
3. What is the difference between data governance and data policy?
Data governance is the overall management of data availability, usability, integrity, and security. A data policy is a specific, documented rule for how data should be handled. Policies are the written rules; governance is the operating system that enforces them.
4. How does a data governance policy support data privacy regulations like GDPR?
A data governance policy establishes clear guidelines for data handling, access control, and accountability. It supports privacy rights through automated consent management, data subject request workflows, and breach notification procedures built directly into the policy.
5. What are the benefits of having a data governance policy?
A documented policy improves data quality, supports regulatory compliance, and improves decision-making by clarifying roles and responsibilities. Enforcing that policy through a governed context layer, rather than a static document, is what turns those rules into something teams and AI agents actually follow day to day.
6. What are the most common pitfalls that cause governance policy failures?
Six come up most often: documentation that’s too long to actually get read, no visible executive sponsorship, policies that ignore how teams already work, training that covers the rule but not the reasoning behind it, no metrics to show whether the policy is working, and manual enforcement that can’t keep pace with modern data volumes. Automating enforcement, rather than relying on periodic manual review, addresses the last one directly.
7. How does Atlan help with data governance policy implementation?
Atlan provides centralized policy management, automated enforcement tied to governed context, and real-time monitoring of policy violations. Policy applies automatically based on sensitivity, lineage, or usage pattern, for both people and AI agents, without manual intervention.
